IPTables misconfigurations can block legitimate traffic, allow unwanted access, or slow down your server. Fixing these issues requires careful troubleshooting. Here’s how to get started:
- Check Rules: Use
sudo iptables -L -v -nto list all rules and spot errors. - Enable Logging: Add a
LOGrule to monitor traffic. Example:sudo iptables -A INPUT -j LOG --log-prefix "DEBUG: ". - Order Matters: IPTables processes rules sequentially. Place specific rules above general ones.
- Backup Rules: Use
sudo iptables-save > /tmp/iptables-backup.rulesto save current configurations. - Monitor Traffic: Use tools like
tcpdumporwatch iptables -nvLfor real-time insights. - Test Incrementally: Apply one rule at a time and verify its impact to avoid locking yourself out.
Key commands for debugging:
iptables -S: View raw rule definitions.iptables -L -t nat: Check NAT table rules.systemctl status iptables: Verify firewall service is active.
Is iptables blocking your traffic? Run sudo iptables -L INPUT -v -n --line-numbers, retry the connection, then run it again: the DROP or REJECT rule whose packet counter went up is the one blocking you. No counter moved? The packet never reached the firewall, so look at the service, the port or the network in front of the server.
Common issues IPTables debugging can resolve:
- Blocked Legitimate Traffic: Fix overly restrictive rules.
- Unwanted Traffic Allowed: Tighten overly permissive rules.
- Performance Problems: Reorder rules and optimize logging.
Common IPTables Rule Problems
Misconfigured IPTables rules can lead to security vulnerabilities and disrupt server connectivity. Understanding these common issues is key to maintaining smooth operations, especially for those hosting their servers on platforms like VPSus. Below, we’ll explore frequent problems caused by poorly configured firewall rules and how they can impact your server.
Blocked Legitimate Traffic
Sometimes, overly restrictive rules can block traffic you actually need. This can lock you out of your server or disrupt critical services. A classic example? Losing SSH access because of a poorly configured INPUT rule. This often happens when administrators forget to allow their own IP address or fail to account for established connections.
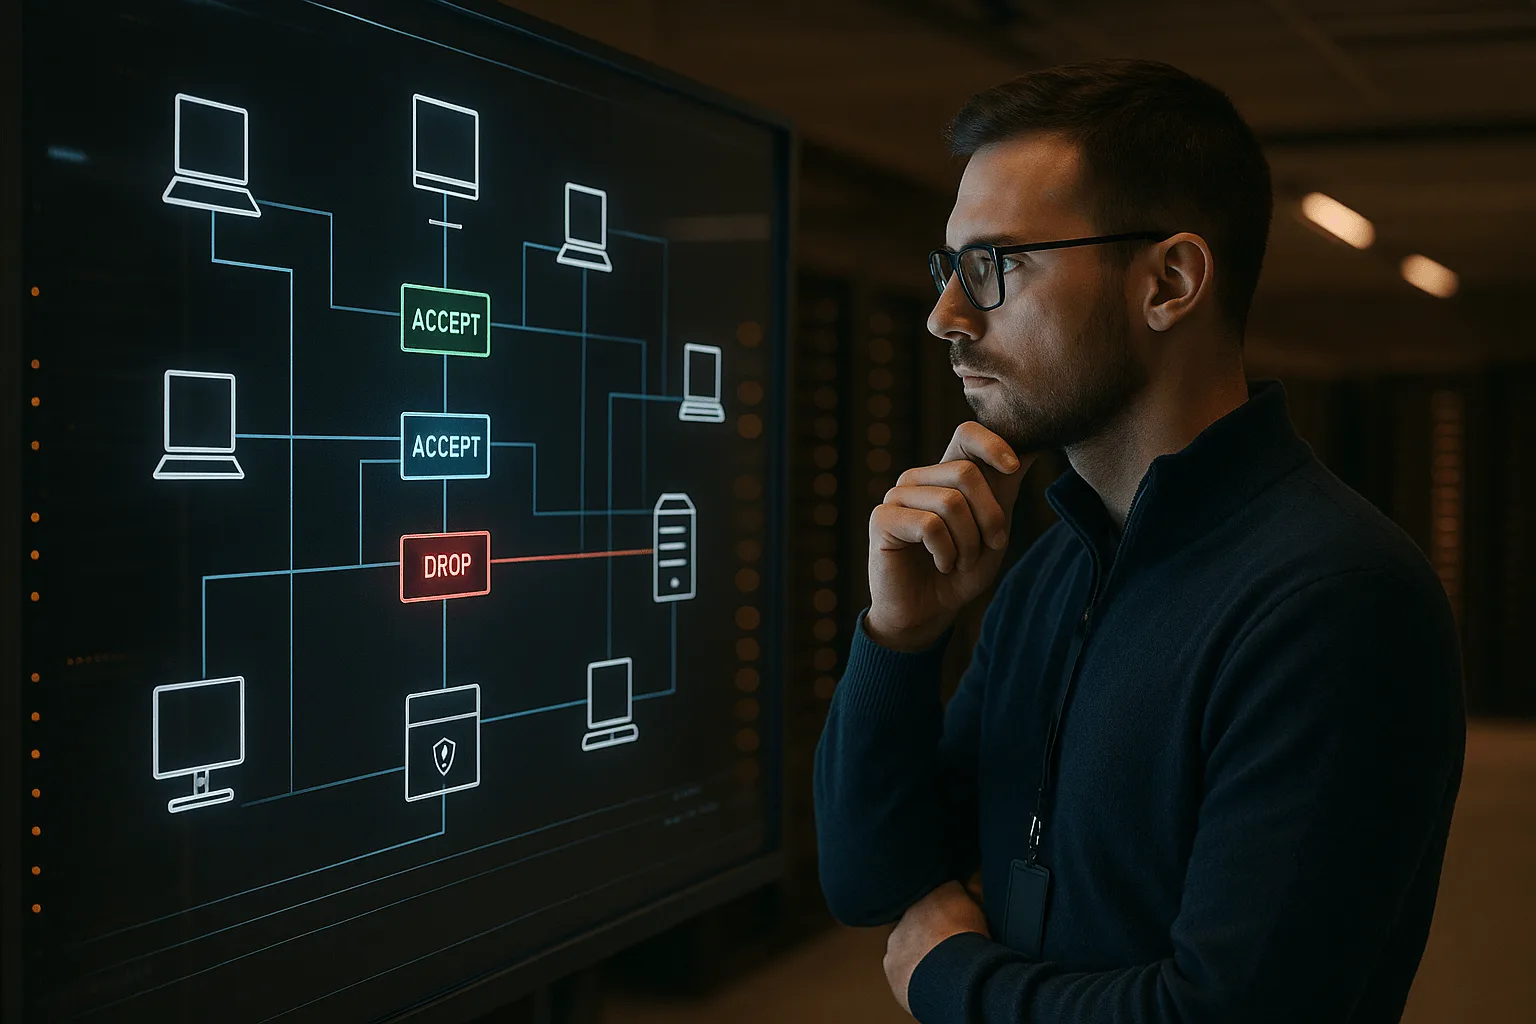
Here’s the catch: IPTables processes rules in order, from top to bottom. If a broad DENY rule is placed early in the chain, it can override more specific ALLOW rules further down. For example, if you block all traffic from a network range but later try to allow a specific IP within that range, the traffic will still be dropped.
Web servers and databases often face similar issues. Restrictive OUTPUT rules, for instance, might block external API connections. Similarly, applications connecting to MySQL (port 3306) or PostgreSQL (port 5432) may fail if the rules don’t account for specific IP ranges or connection patterns.
Testing and carefully organizing your rules can help avoid these headaches. When troubleshooting, always remember: the order of your rules matters.
Unwanted Traffic Allowed
On the flip side, overly permissive rules can leave your server exposed to attacks. Research shows that human error, including firewall misconfigurations, is behind 95% of data breaches.
Default settings often open the door too wide. For instance, allowing SSH (port 22) access from any IP instead of restricting it to trusted networks increases your attack surface. Port range misconfigurations are another common mistake. If you accidentally open a range of ports (e.g., “–dport 80:443”) instead of a single port, you might expose services you didn’t intend to.
“Bad actors use automation to scan the internet and continuously test for misconfigurations. They rely on overly permissive rules that can provide an easy avenue to exploit.”
– Tim Woods, VP of Technology Alliances, FireMon
Outdated or unused rules also pose risks. Many organizations find that 30–40% of their firewall policies are no longer needed, yet these rules often remain in place, creating exploitable gaps. Similarly, rules using ‘0.0.0.0/0’ expose services to all internet traffic. While this might be fine for public-facing web servers, it’s risky for administrative tools or internal apps.
Cleaning up unnecessary rules and tightening permissions can significantly reduce vulnerabilities.
Connectivity and Performance Problems
Poorly optimized rules don’t just create security risks – they can also hurt performance. When frequently matched rules are buried at the bottom of a long chain, it adds unnecessary latency.
Excessive logging is another pitfall. While logging is useful for monitoring, too much of it can overwhelm system resources and slow down network processing.
Connection state tracking is also crucial. Without properly using “–state ESTABLISHED,RELATED” rules, your firewall may evaluate every packet individually, leading to inefficiencies. Similarly, ignoring packet fragmentation can result in incomplete data transfers or connection timeouts.
DNS resolution issues often arise when OUTPUT rules block DNS queries or responses. Even if your service connections are allowed, applications may experience slow responses or timeouts if DNS lookups are delayed.
Lastly, conflicting rules can cause inconsistent behavior. This often happens when multiple administrators make changes without coordination or when automated tools introduce rules that clash with manual configurations.
In VPS setups – especially those with multiple services, containers, and dynamic IPs – carefully planning your IPTables rules is essential. Recognizing these common problems can help you troubleshoot effectively and keep your server running smoothly.
Key Commands for Debugging IPTables
When troubleshooting IPTables, the right commands can make all the difference. They help you examine active rules, check service status, and monitor traffic in real time. Let’s break it down.
Listing and Viewing Rules
To see the rules exactly as they were created, use sudo iptables -S. This outputs the commands that set up your rules, making it easier to recreate or tweak them. For example, you might see something like -P INPUT DROP or -A INPUT -m conntrack --ctstate RELATED,ESTABLISHED -j ACCEPT.
For a more structured view, try sudo iptables -L. This displays rules in a table format with columns for target, protocol, source, destination, and more. It’s a great way to quickly spot patterns or conflicts.
Need more detail? Add flags like -v for verbose output (showing packet counts, interface names, and rule options) and -nto display IPs numerically instead of resolving hostnames. A command like sudo iptables -L -v -n gives you a full, detailed overview.
IPTables manages five tables: filter, nat, mangle, raw, and security. By default, commands only show the filter table. To view NAT rules, for example, you’d need to specify it explicitly with sudo iptables -t nat -L.
If you’re only interested in a specific chain, you can narrow the output. Use commands like sudo iptables -L INPUT or sudo iptables -S OUTPUT to focus on the chain you want to investigate.
Once you’ve reviewed the rules, it’s time to check whether the firewall service is running as expected.
Checking IPTables Service Status
Before diving into the rules, make sure the IPTables service is active. On most modern Linux systems using systemd, run systemctl status iptables. That unit comes with the iptables-services package on RHEL-family systems; on Debian and Ubuntu, rules are loaded at boot by netfilter-persistent, so check systemctl status netfilter-persistent there. This will tell you whether the service is running, when it was last started, and if it’s set to start automatically at boot. It also flags any recent errors.
If you’re working on an older system with sysvinit, use service iptables status instead.
Some systems use firewalld as a higher-level interface for IPTables. If that’s the case, check its status with systemctl status firewalld.
Keep in mind, an active service doesn’t necessarily mean your rules are working. Missing kernel modules or misconfigured rules can still cause issues, so the status check is just the first step in diagnosing problems.
Logging and Monitoring Traffic
Once you’ve confirmed the rules and service status, it’s time to monitor traffic. IPTables logging captures detailed packet information, including source and destination IPs, protocols, and ports.
To enable logging, add a LOG target to your rules. For example, sudo iptables -A INPUT -j LOG --log-prefix "iptables: " --log-level 4 will log all incoming packets with a clear prefix for easier filtering later.
Logs are typically stored in /var/log/messages or /var/log/syslog, depending on your Linux distribution. Use sudo tail -f /var/log/messages (or sudo journalctl -k -f on systems without a syslog file) to watch log entries appear in real time.
For high-traffic systems, rate limiting is critical to prevent log flooding. Without the --limit flag, busy servers can generate thousands of log entries per second, making analysis overwhelming and consuming disk space quickly.
Want to see live updates on rule activity? Use sudo watch iptables -nvL INPUT. This refreshes the rule display every two seconds, showing packet counters and revealing which rules are being triggered most often.
If you’re troubleshooting a specific issue, like SSH connectivity, create temporary logging rules targeting that traffic. For instance, use this command: sudo iptables -I INPUT -p tcp --dport 22 -j LOG --log-prefix "SSH-DEBUG: ". It logs detailed information about SSH attempts without interfering with other traffic.
For VPS environments, such as those offered by VPSus, logging becomes even more important. With multiple services running across various ports and protocols, and traffic coming from all over the world, detailed logs help you differentiate between legitimate connections and potential threats.
Step-by-Step Debugging Methods
Debugging IPTables effectively requires a careful, step-by-step approach. By making one change at a time and testing immediately, you can avoid accidentally blocking critical services or locking yourself out of your server.
Incremental Rule Testing
Before diving into changes, back up your current rules with:
sudo iptables-save > /tmp/iptables-backup.rules
Then, test one rule at a time. If you suspect a particular rule is causing issues, you can temporarily modify it. For example, if an SSH connection is being blocked by a DROP rule, you can add a more permissive rule above it:
sudo iptables -I INPUT 1 -p tcp --dport 22 -j ACCEPT
After each change, test the affected service. Try connecting, pinging, or running the functionality you’re troubleshooting. If the issue persists, you’ll know the problem lies elsewhere.
For remote servers, such as VPS instances, set up a safety net before you touch the live rules. The cleanest one is iptables-apply: it loads a rules file, asks you to confirm, and rolls back to the previous rules when the timeout expires because the change cut your session:
sudo iptables-save > /tmp/iptables-test.rules
# edit /tmp/iptables-test.rules, then:
sudo iptables-apply -t 60 /tmp/iptables-test.rules
If you change rules one command at a time instead, schedule a restore of the backup you just took, not a flush: iptables -F deletes the rules but keeps the chain policy, so a server with -P INPUT DROP stays locked out after a flush:
echo "*/10 * * * * root /usr/sbin/iptables-restore < /tmp/iptables-backup.rules" | sudo tee /etc/cron.d/iptables-restore
Don’t forget to remove this cron job (sudo rm /etc/cron.d/iptables-restore) once debugging is complete. After testing rules incrementally, logging can help you dig deeper into the problem.
Adding Logging Rules
Logging rules can provide a clear picture of how packets are being processed. Placing these rules strategically allows you to track specific traffic and understand why certain packets are being dropped or allowed.
To log specific traffic, duplicate the rule and set the target to LOG. For example, to investigate dropped HTTP traffic:
sudo iptables -A INPUT -p tcp --dport 80 -j LOG --log-prefix "HTTP-DEBUG: " --log-level info
For even more detailed tracking, use the TRACE target (available in recent kernels). TRACE logs every rule that matches a packet as it moves through tables and chains. For example:
sudo iptables -t raw -A PREROUTING -p tcp --destination 192.168.0.0/24 --dport 80 -j TRACE
sudo iptables -t raw -A OUTPUT -p tcp --destination 192.168.0.0/24 --dport 80 -j TRACE
“This target marks packets so that the kernel will log every rule which matches the packets as they traverse the tables, chains, rules.” – Zoredache, Server Fault
With iptables-legacy, TRACE lines go to the kernel log (/var/log/kern.log, or sudo journalctl -k) and look like this:
TRACE: raw:PREROUTING:policy:2 IN=eth0 OUT= MAC=00:1d:7d:aa:e3:4e:00:04:4b:05:b4:dc:08:00 SRC=192.168.32.18 DST=192.168.12.152 LEN=52 TOS=0x00 PREC=0x00 TTL=128 ID=30561 DF PROTO=TCP SPT=53054 DPT=80
If iptables -V prints (nf_tables), your iptables runs on the nftables backend and TRACE events are not written to the kernel log. Watch them with sudo xtables-monitor --trace instead (see the TRACE target in the iptables-extensions man page).
Be precise when using TRACE to avoid overwhelming your system with logs, and disable these rules as soon as you’re done.
To see which rules are actively processing traffic, use:
sudo iptables -L -v
This command displays packet and byte counters, helping you identify active rules and spot redundant ones with zero counters. If further validation is needed, packet capture tools can provide deeper insights.
Packet Capture Tools
Packet capture tools are invaluable for analyzing actual network traffic.
Tcpdump is a simple yet powerful tool for quick traffic checks. To monitor all traffic on port 22, use:
sudo tcpdump -i any port 22 -n
To filter traffic for a specific IP and port:
sudo tcpdump -i eth0 host 203.0.113.45 and port 80 -v
For more detailed analysis, use Wireshark. While it’s typically GUI-based, you can use tcpdump to capture packets remotely and analyze them locally:
sudo tcpdump -i eth0 -w /tmp/debug.pcap port 443
Download the .pcap file and open it in Wireshark for an in-depth look at protocol details.
If you prefer command-line tools, Tshark, the CLI version of Wireshark, offers robust filtering options. For example:
sudo tshark -i eth0 -f "tcp port 80" -T fields -e ip.src -e ip.dst -e tcp.flags
On high-traffic servers, use capture filters to focus on relevant data. For instance, to capture only new SSH connection attempts:
sudo tcpdump -i eth0 'tcp[tcpflags] & tcp-syn != 0 and port 22'
Best Practices for Managing IPTables
Managing IPTables effectively goes beyond simple debugging, especially when dealing with remote servers like VPS instances. If you’re hosting on platforms such as VPSus, following these practices is crucial to keeping your firewall secure and functional. Below are some key strategies to maintain a reliable and efficient IPTables configuration.
Backup and Documentation
Backing up your rules is a must to avoid losing them during reboots or unexpected system failures.
Before you edit anything, take a dated copy of the live rules. iptables-save works the same on every distribution; on RHEL-family systems (AlmaLinux, Rocky Linux — CentOS Linux 7 reached end of life on 30 June 2024), check systemctl status firewalld too, because firewalld usually manages the rules there:
sudo iptables-save > /root/iptables-$(date +%F).rules
On Debian and Ubuntu systems, save the rules to the file that is loaded at boot:
sudo iptables-save > /etc/iptables/rules.v4
To reload them automatically after a reboot, install iptables-persistent: its netfilter-persistent service loads /etc/iptables/rules.v4 at boot, and netfilter-persistent save writes the current rules back. (An /etc/network/if-pre-up.d script only runs on systems that still bring interfaces up with ifupdown.)
sudo apt install iptables-persistent
sudo netfilter-persistent save
It’s a good habit to regularly back up your rules and include detailed comments for easier troubleshooting later. For example:
sudo iptables -A INPUT -p tcp --dport 8080 -m comment --comment "Allow Jenkins CI server access" -j ACCEPT
Finally, verify that your rules load properly after a reboot to avoid surprises.
Use Atomic Writes
When updating IPTables, atomic operations prevent the half-applied ruleset you get when a script dies between two iptables commands. Write the complete ruleset to a file and load it with iptables-restore (for example sudo iptables-restore < /etc/iptables/rules.v4): the table is replaced in one step, and a bad line aborts the load instead of leaving half the rules in place.
The -w flag solves a different problem, concurrent changes:
sudo iptables -w -A INPUT -p tcp --dport 443 -j ACCEPT
It makes iptables wait for the xtables lock instead of exiting when another process (Docker, fail2ban, a firewall manager) holds it at the same moment.
Understand Rule Order
The order of your rules matters – a lot. IPTables processes rules one by one and stops as soon as it finds a match. This means the sequence of your rules directly impacts both security and performance.
Specific rules should always come before general ones. For example, if you want to block a specific IP but allow a larger subnet, structure your rules like this:
# Block the specific IP first
sudo iptables -A INPUT -s 192.168.1.100 -j DROP
# Then allow the broader subnet
sudo iptables -A INPUT -s 192.168.1.0/24 -j ACCEPT
If you reverse this order, the broader rule would allow traffic from the specific IP before the block rule can take effect.
End your chains with a default “deny all” rule to block any traffic not explicitly allowed:
sudo iptables -A INPUT -j DROP
Add it only after the ACCEPT rules for loopback, ESTABLISHED,RELATED connections and your SSH port; on a remote server, that line without them is the lockout.
To optimize performance, place frequently matched rules at the top of the chain. For example, if a rule matches 90% of your traffic but is buried deep in the chain, every packet will waste time going through unnecessary checks. Reordering such rules can significantly reduce processing overhead.
Additionally, keep an eye on your rules with iptables -L -v. This command lets you inspect packet counters, helping you identify rules with zero matches, which might be redundant or misplaced.
Conclusion
Debugging IPTables requires a methodical approach, relying on small, incremental adjustments and a solid backup strategy. Whether you’re working on a local setup or a remote system, the process remains the same: test changes step by step and always have a backup ready.
One key principle to keep in mind is the sequential nature of IPTables rules. When troubleshooting, avoid making broad changes that might complicate things further. Instead, use logging rules with clear, descriptive prefixes to track traffic behavior. Resetting counters with iptables -Z can also help you get accurate packet counts for better analysis.
For real-time insights, the watch command is an excellent tool, and pairing it with tcpdump can help confirm whether packets are reaching your server as intended.
If SSH itself is the problem rather than the firewall, our guides to fixing “Permission denied (publickey)” and to SSH key security pick up where this one stops.
Last verified November 2026: commands and options checked against the iptables 1.8 man pages (iptables, iptables-extensions, iptables-apply) and Debian’s netfilter-persistent.